Digital Forensics Lab · Case CC-2026-017

The Parking Lot Stick

A USB stick was found in the parking lot of Crumble & Co. You are the forensic examiner. Acquire it properly, then find out who it belongs to and what it holds.

1 Briefing

INTERNAL MEMO – CONFIDENTIAL
From: Head of Corporate Security, Crumble & Co.
To: Forensic Examiner (you)
Re: Case CC-2026-017 – USB stick found on company premises

On 2026-10-12 14:35, Parking Lot P2, Row 4, a USB stick was found by Sarah Jensen (#314), Corporate Security. Nobody has reported it missing.

This comes at a bad time. A competitor recently launched a product that looks a lot like our best-selling cookie, and R&D suspects that confidential recipe information has left the building. The stick may be unrelated, but we cannot rule anything out.

Ms Jensen bagged and labelled the stick right away. It has not been plugged into any computer. Please:

  1. Take over the evidence and document the handover in the chain of custody.
  2. Make a forensically sound image of the stick and verify it with hashes.
  3. Analyse the image: who owns the stick, what is (and was) on it, and does it relate to the suspected leak?
  4. Write a report that a non-technical manager can follow and that would hold up in a labour-court hearing.

The detailed questions, deliverables and deadline are in the assignment on Moodle.
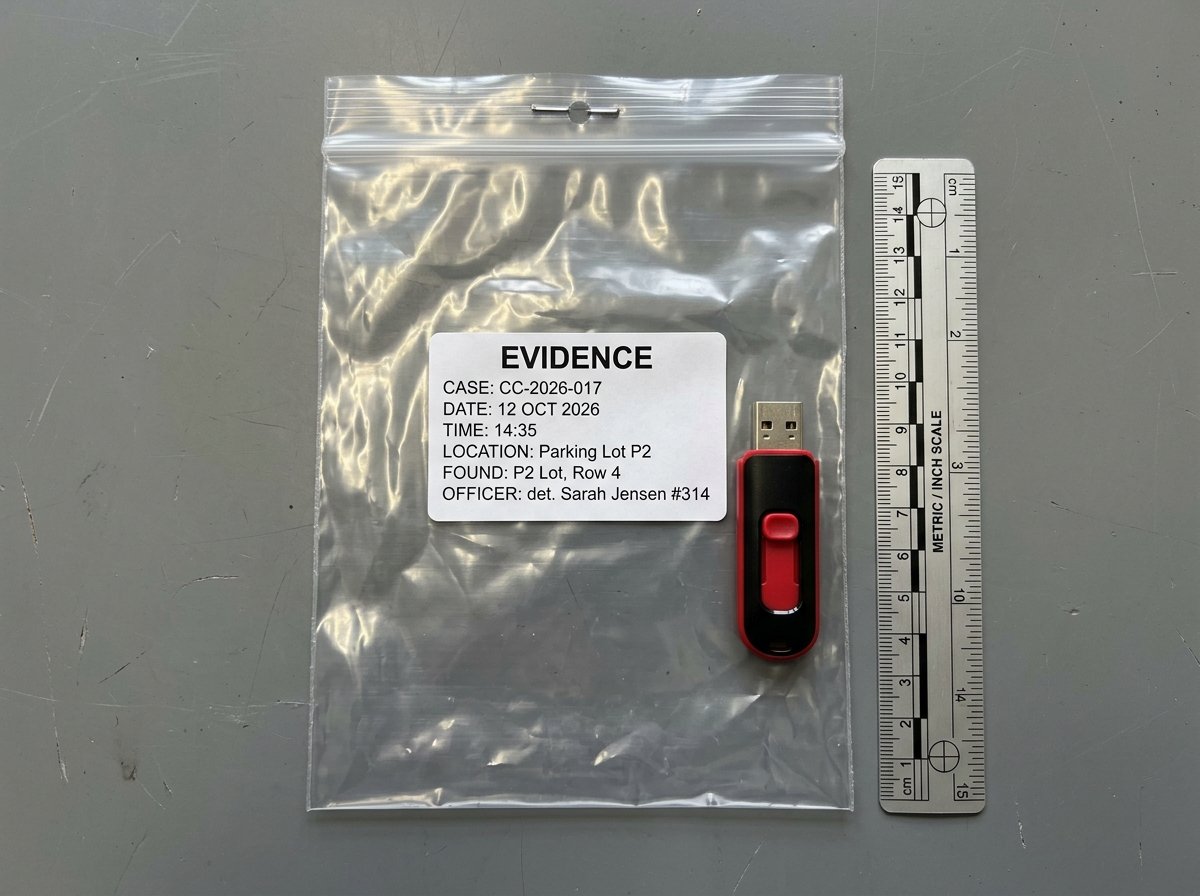
Sealed evidence bag with a red and black USB stick, an evidence label for case CC-2026-017 and a forensic scale ruler
Exhibit
CC-2026-017-01
Item
USB flash drive, SanDisk Cruzer Blade
Capacity
64 MiB
Found
2026-10-12 14:35, Parking Lot P2, Row 4

Rules of engagement

  • Never work on the original. Attach it only through a write blocker and analyse a verified copy.
  • Hash before and after. The source and the image must have the same hash, and you write the hash down.
  • Document everything. Every handover, command and finding gets a time and a name.
  • Stay objective. Report what the evidence shows, how you found it and how sure you are. Don't report what you believe.

Want to see the structures byte by byte?

See how real partition tables and file systems look byte by byte: File Systems in Hex: MBR, GPT, FAT32, ext4, NTFS →

Going further: deep-dives into multimedia forensics → and mobile forensics →

2 Chain of Custody

Each time the exhibit changes hands, add a row. Print this form or copy it into your report. The first entry was made by the finder.

#Date / timeReleased byReceived byPurpose / actionSeal intact?
12026-10-12 14:35– (found)Sarah Jensen #314, Corp. Security Found in Parking Lot P2, Row 4; bagged and labelled on sitesealed
2
3
4
5

3 Acquisition Lab

The stick is now attached to your forensic workstation. This simulated terminal behaves roughly like Linux. Identify the device, protect it from writes, image the whole device and prove that the copy is exact. Type help to see the available commands.

examiner@forensic-ws: ~/case

4 Evidence Image

🔒 Finish the acquisition lab to unlock the verified image.